Keeping clients' computers safe and profitable for over 30 years
Home Forms About Current Newsletter subscribe
Problems because AI is helping to find decades of problems
|
 |
The most common way to track security flaws is through CVEs. The U.S. Department of Homeland Security has an agency called CISA (Cybersecurity and Infrastructure Security Agency). They sponsor a "Common Vulnerabilities and Exposures” database, which assigns a unique number to each newly confirmed vulnerability. So, when I say Microsoft had 974 CVEs patched in September, I'm saying that 974 uniquely numbered flaws were reported, confirmed, and numbered by CISA.
Examples of other companies:
- Oracle—1,449 security patches in July.
- Google Chrome — 230 security fixes on September 8.
- Adobe—172 CVEs on September 8.
- Samsung—90 vulnerabilities patched in September
- Cisco — 46 CVEs patched in August
- Qualcomm—16 CVEs in September.
The time from reporting to infecting is shrinking
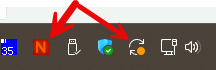
This is ultimately good. These AI tools are also being used during the initial coding process to make software more secure. The downside is that they are also being used by miscreants to create malware to infect our systems. Not only are we being required to patch more software more often, but we also have to do it faster. Miscreants are using AI to help analyze the patches and see what they fix. Then they can create malware to exploit unpatched systems quicker. That means we need to patch quicker. When you see your green Ninite icon turn red, apply the patches that day. And when the Windows update icon shows the two circular arrows, you need to apply the Microsoft update as soon as possible.
The Great Debate
An interesting debate is engaging security researchers. Is the rash of new vulnerabilities a one-time event, which in a few months will be over and our software will be cleaner, safer, and require fewer patches? Or will AI continue to get smarter and find more flaws, so the end is not in sight? Are we going to get safer or be stuck in a downward spiral? I have no opinion on this matter but find it fun to watch.
Further Information
- Brian Krebs on Microsoft's September patches
- The CVE Program from CISA, America's Cyber Defense Agency.
- A nice 3-minute basic tutorial on AI and security.

This article is licensed under a Creative Commons Attribution-NoDerivs 3.0 Unported License.